Anugal logo
  • Home
  • Platform
    • Joiner–Mover–Leaver (JML) Automation

      Automated lifecycle changes, zero delays

      Birthright & Role Mapping

      Right access from day one.

      Third-Party Identity Governance

      Control non-employee access seamlessly.

      Machine & Non-Personal Identity Management

      Govern service and machine identities.

      Self-Service Access Requests

      Fast requests with built-in controls

      Approval & Access Control Engine

      Policy-driven approvals, consistent enforcement.

      Emergency Access (Firefighter)

      Secure, time-bound privileged access.

      Mass & Bulk Access Requests

      Manage access changes at scale

      Access Discovery

      Enterprise-wide visibility into access

      AI-Based Access Recommendations

      AI-guided access decision support

      Role Design & Optimization

      Optimized roles and entitlement structure

      My Access / My Entitlements

      User view of assigned access

      Insights (Compliance & Security)

      Clear visibility into access risk.

      Segregation of Duties (SoD) Engine

      Prevent conflicts before violations

      Reports & Audit Trails

      Audit-ready evidence, always available

      Access Certifications

      Periodic reviews with full traceability.

      Orchestration Studio

      Design identity workflows visually

      Job Scheduler

      Automate recurring identity operations.

      Third-Party & Service Integrations

      Connect systems without disruption

      Anugal Co-Pilot

      Conversational access governance interface

      Anugal.AI (Agentic Architecture)

      Agent-driven identity orchestration layer

  • Solutions
    • Automate Joiner-Mover-Leaver (JML) Lifecycle

      Lifecycle-driven governed access automation

      Simplify Access Requests & Approvals

      Structured, policy-driven access decisions

      Enforce Segregation of Duties (SoD)

      Prevent conflicting access before execution

      Accelerate Access Reviews & Certifications

      Context-driven certification and review automation

      Manage Machine & Third-Party Access

      Govern non-human and external identities

      Gain Real-Time Access Intelligence

      Continuous visibility into identity risk

      SAP IDM Migration

      Move off SAP IdM before 2027 with governance intact

      SAP GRC Transition

      Plan your GRC 12.0 move without losing controls

      Replace or Extend: Microsoft Entra

      Entra ID Governance and SAP: two routes, one decision

      Banking & Financial Services (BFSI)

      Govern financial access across systems

      Healthcare & Life Sciences

      Secure clinical and research access

      Manufacturing

      Control plant and operational identities

      Retail

      Govern distributed workforce access

      Consumer Goods

      Secure supply chain identity operations

      Public Sector

      Control access across government systems

      SOX

      Financial access control and auditability

      GDPR

      Privacy-driven identity access governance

      HIPAA

      Protect healthcare access and data

      PCI-DSS

      Secure payment system access controls

      NIS2

      Strengthen cyber resilience governance

      GxP

      Controlled access for regulated environments

      Security & Risk Leaders

      Prevent identity risk before exposure

      Access & Identity Managers

      Centralized lifecycle and access control

      Compliance & Audit Teams

      Continuous audit-ready governance evidence

      IT Operations & Support

      Reduce manual access administration

      Business & Application Stakeholders

      Accountable ownership of business access

  • Why Anugal
    • ROI Calculator
    • Time to Value
    • Agentic IGA Platform
    • Integration Catalog
    • Anugal vs Legacy vs Manual
  • Resources
    • Blog
    • Product Tours
    • Solution Briefs
    • White Papers
    • Help Center
    • IGA Knowledge Hub
  • Company
    • Our Story
    • Partner with Us
    • Newsroom
    • Events
    • Success Stories
      • Terms and Conditions
  • Request Demo
Preventive SoD for SAP: four ways a conflict passes Entra package checks, and a check before provisioning
CategoriesSAP Security & GRC
November 19, 2026

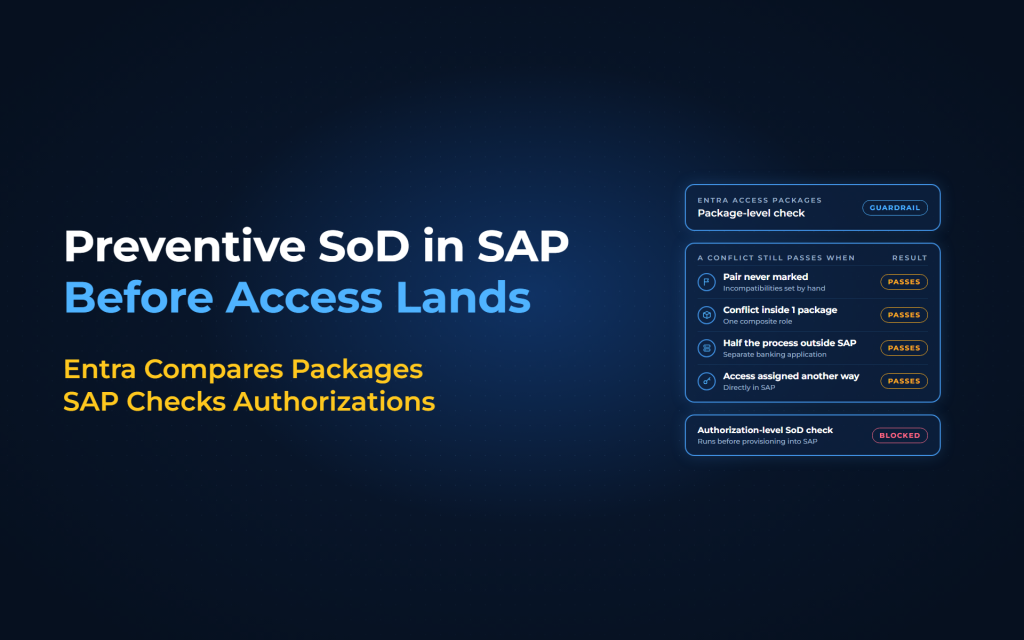
Why Preventive SoD Must Run Before Access Is Granted, and Where Entra Stops

Microsoft Entra can block incompatible access packages, but Microsoft sends fine-grained SAP SoD checks to other products. Here is why SoD has to run at request time, at the authorization level and across SAP and non-SAP systems.
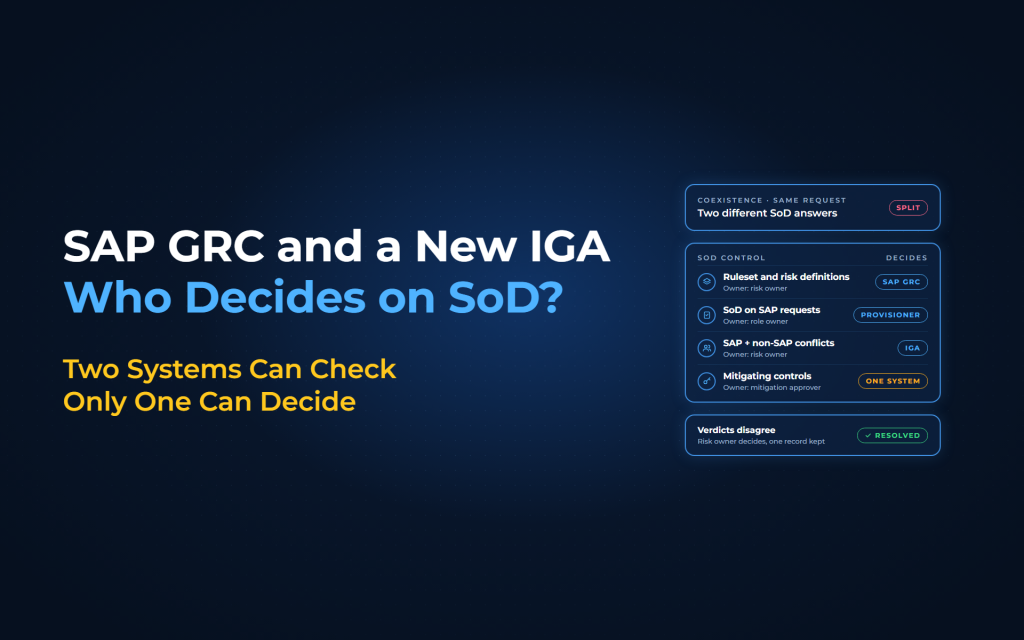
SAP GRC and IGA coexistence: one deciding system, one owner and one record for each SoD control
CategoriesSAP Security & GRC
November 19, 2026

Who Decides on SoD When SAP GRC and a New IGA Run Side by Side?

When SAP GRC and a new IGA run side by side, 1 request can get 2 SoD verdicts. Give each control 1 deciding system, 1 owner and 1 evidence record, and send every disagreement to the risk owner.

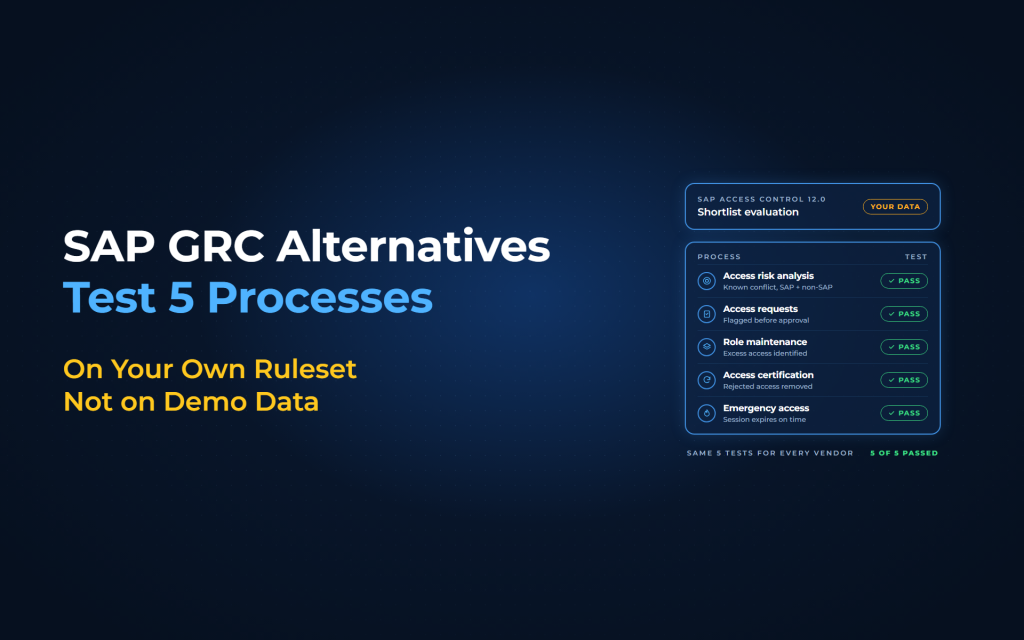
SAP GRC alternatives scorecard: test risk analysis, requests, roles, reviews and firefighter access on your data
CategoriesSAP Security & GRC
November 19, 2026

5 Processes to Test When You Evaluate SAP GRC Alternatives

Feature checklists all say yes. Test SAP GRC alternatives on the 5 processes SAP Access Control runs today, on your own ruleset, and choose on evidence.

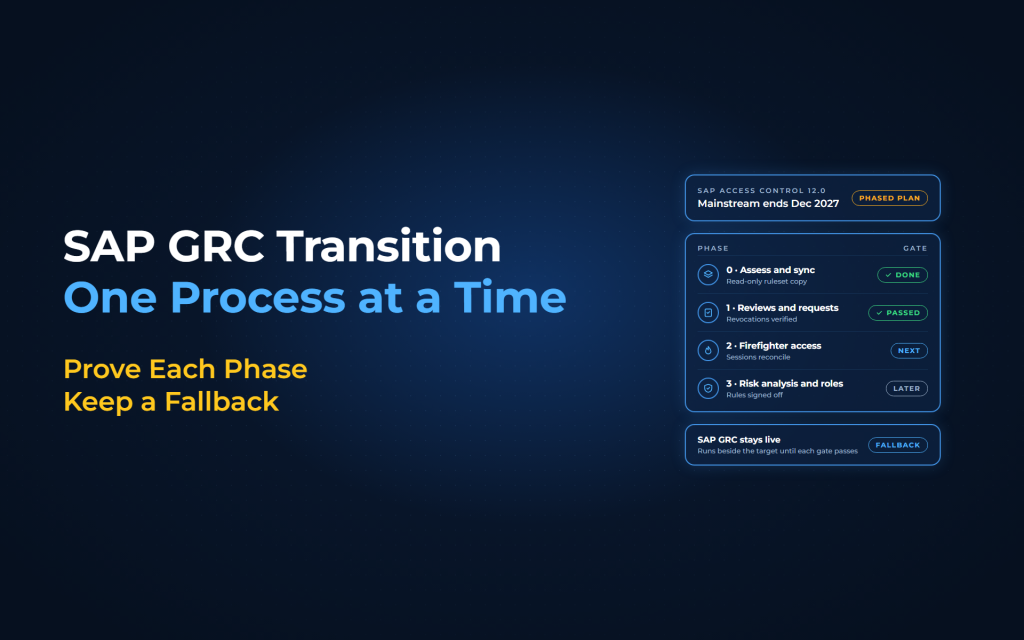
Phased SAP GRC transition: access reviews and requests first, firefighter access second, risk analysis last
CategoriesSAP Security & GRC
November 13, 2026

Which Process to Move First in an SAP GRC Transition

Moving every SAP GRC process in a single cutover risks audit gaps. Move access reviews and requests first, firefighter access second and the ruleset last, and prove each phase before the next.

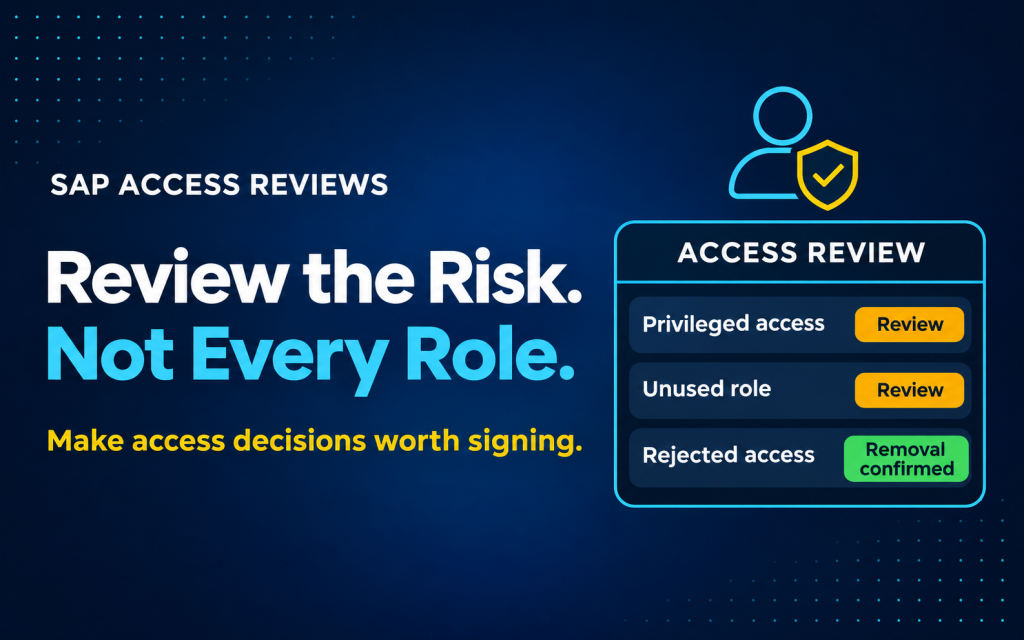
SAP access reviews
CategoriesSAP Security & GRC
November 6, 2026

SAP Access Reviews: Stop Asking Managers to Approve Everything

A completed SAP access review is not proof of the right access. Give reviewers context, prioritize risk, and prove rejected access was removed.

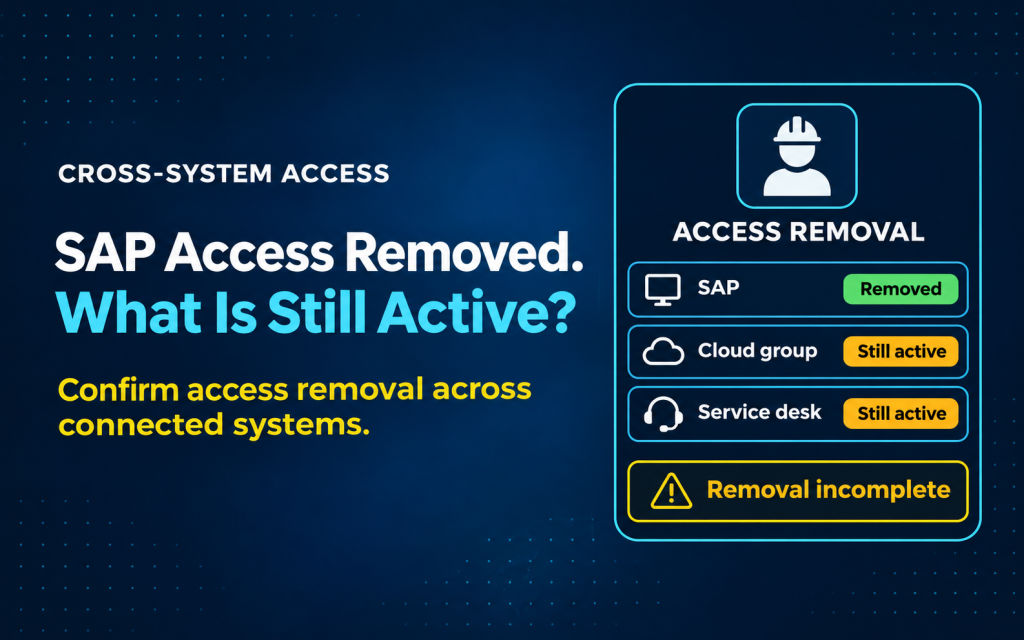
Access Removal Across Connected Systems
CategoriesSAP Security & GRC
November 6, 2026

Your Biggest SAP Access Risk May Sit Outside SAP

An SAP GRC version change does not remove access from every connected application. Test one contractor exit to find the cross-system gaps.

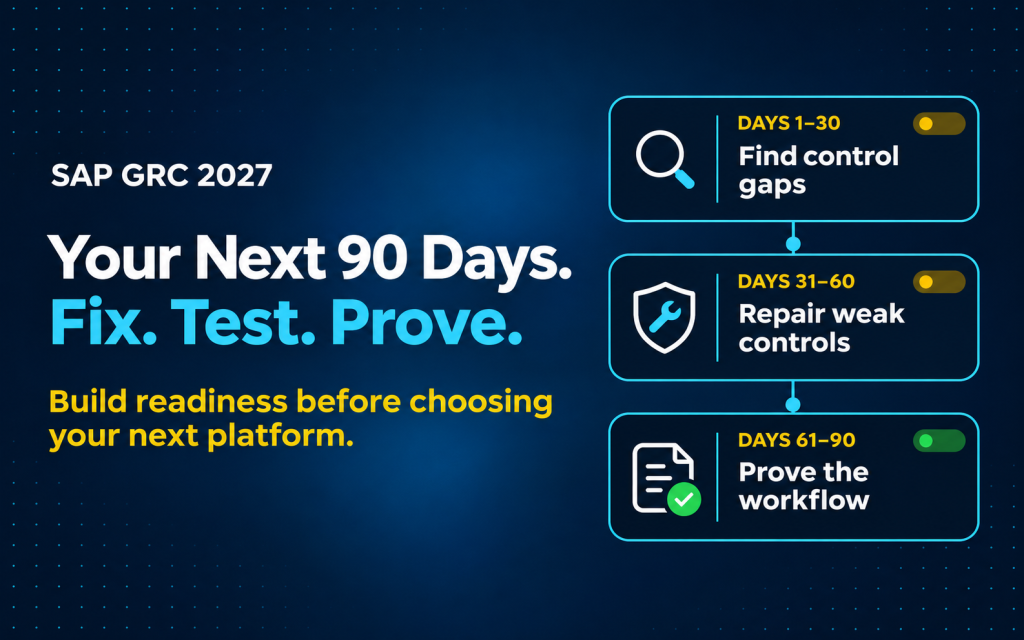
SAP GRX 90 days readiness plan
CategoriesSAP Security & GRC
November 6, 2026

SAP GRC 2027: What to Fix in the Next 90 Days

A 90-day SAP GRC 2027 readiness plan: find the control gaps, repair the weakest decisions, and prove the workflow before choosing a platform.

SAP GRC 2027 options: upgrade on the SAP path, extend maintenance to bridge the transition, or modernize access workflows
CategoriesSAP Security & GRC
November 6, 2026

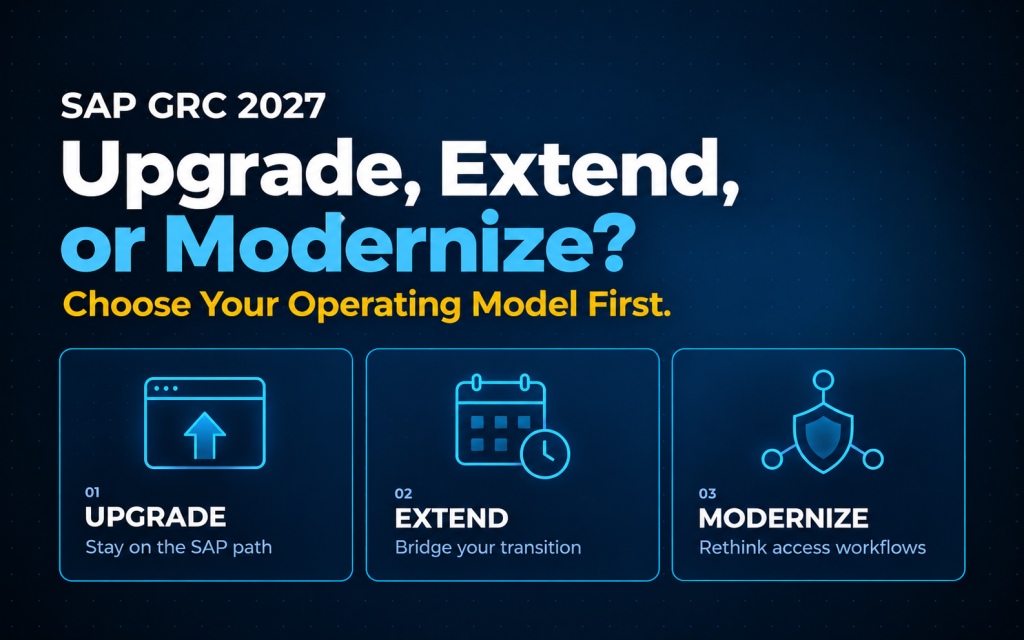
SAP GRC 2027: Upgrade, Extend, or Modernize?

Upgrade within SAP, use extended maintenance as a bridge, or modernize selected access workflows. Choose the operating model before the tool.

SAP firefighter access: why a session log is not enough for audit
CategoriesSAP Security & GRC
November 6, 2026

Your SAP Access Request Was Approved. Was It Controlled?

SAP GRC 2027 · Article 3 of 8 · Quick Read SAP Firefighter Access: A Log Is Not Enough Emergency access is only controlled when someone can explain what happened. An urgent production issue appears at 11:30 p.m. An engineer receives firefighter access, fixes the incident, and closes the ticket. Weeks later, audit asks: Who […]

SAP firefighter access: why a session log is not enough for audit
CategoriesPrivileged Access Management, SAP Security & GRC
November 6, 2026

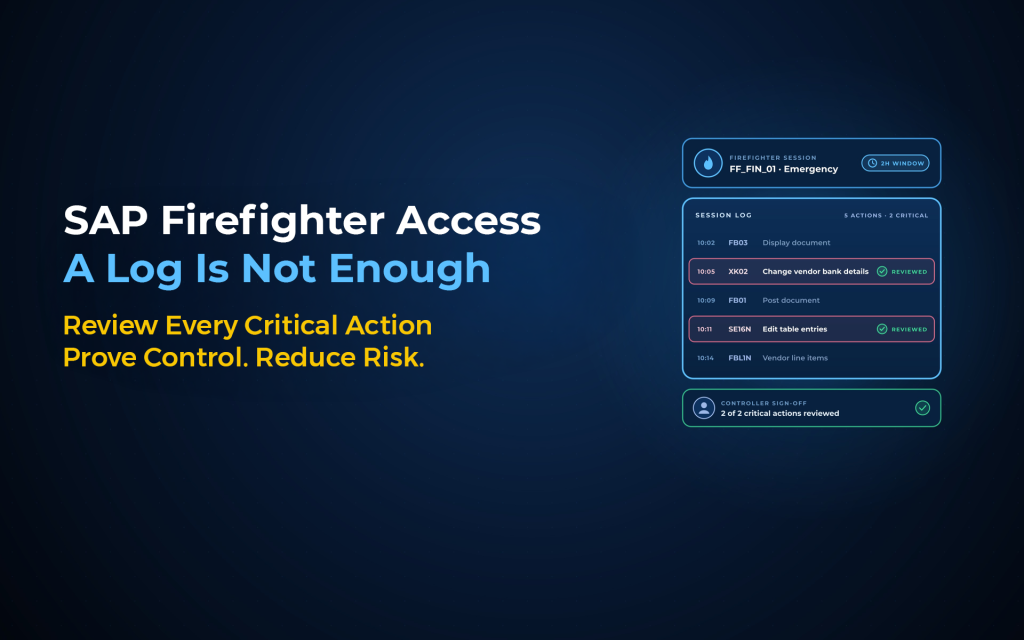
SAP Firefighter Access: A Log Is Not Enough

SAP GRC 2027 · Article 3 of 8 · Quick Read SAP Firefighter Access: A Log Is Not Enough Emergency access is only controlled when someone can explain what happened. An urgent production issue appears at 11:30 p.m. An engineer receives firefighter access, fixes the incident, and closes the ticket. Weeks later, audit asks: Who […]

Posts pagination

  • 1
  • 2

Recent Posts

  • Why Preventive SoD Must Run Before Access Is Granted, and Where Entra Stops
  • Where Each SAP IDM Feature Lands in Microsoft Entra
  • Who Decides on SoD When SAP GRC and a New IGA Run Side by Side?
  • How to Prove Who Had SAP Access When a DORA Incident Happened
  • How to Decommission SAP IDM Without Losing Your Audit Trail

Recent Comments

No comments to show.

Explore Our Modern
IGA Platform Today

Evaluate, experience, and move forward with confidence. Get a customized
Anugal demo designed for smooth, real-world operations.

Book A Demo alt

Secure. Access. Govern

Secure. Access. Govern

Secure. Access. Govern

Secure. Access. Govern

Secure. Access. Govern

Secure. Access. Govern

Platform

  • Identity Lifecycle Management
  • Joiner–Mover–Leaver (JML)
  • Birthright & Role Mapping
  • Third-Party Identity Governance
  • Machine & Non-Personal Identity Management
  • Access Requests & Controls
  • Self-Service Access Requests
  • Approval & Access Control Engine
  • Emergency Access (Firefighter)
  • Mass & Bulk Access Requests
  • Access Intelligence
  • Access Discovery
  • AI-Based Access Recommendations
  • Role Design & Optimization
  • My Access / My Entitlements
  • Identity & Access Governance
  • Insights (Compliance & Security)
  • Segregation of Duties (SoD) Engine
  • Reports & Audit Trails
  • Access Certifications
  • Integration & Automation
  • Orchestration Studio
  • Job Scheduler
  • Third-Party & Service Integrations
  • AI Agents
  • Anugal Co-Pilot
  • Anugal.AI (Agentic Architecture)

Solution

  • By Use Case & Outcome
  • Automate Joiner-Mover-Leaver (JML) Lifecycle
  • Simplify Access Requests & Approvals
  • Enforce Segregation of Duties (SoD)
  • Accelerate Access Reviews & Certifications
  • Manage Machine & Third-Party Access
  • Gain Real-Time Access Intelligence
  • By Industry
  • Banking & Financial Services (BFSI)
  • Healthcare & Life Sciences
  • Manufacturing
  • Retail
  • Consumer Goods
  • Public Sector
  • By Regulation
  • SOX
  • GDPR
  • HIPAA
  • PCI-DSS
  • NIS2
  • GxP
  • By Role
  • Security & Risk Leaders
  • Access & Identity Managers
  • Compliance & Audit Teams
  • IT Operations & Support
  • Business & Application Stakeholders

Solutions

  • By Use Case & Outcome
  • By Industry
  • By Regulation
  • By Role

why anugal

  • ROI Calculator
  • Time to Value
  • Integration Catalog
  • Agentic IGA Platform
  • Anugal vs Legacy vs Manual

Company

  • Our Story
  • Partner With Us
  • Newsroom
  • Events
  • Success Stories

Resources

  • Blog
  • Product Tours
  • White Papers
  • Help Center
  • Solution Briefs

Others

  • IGA
  • Terms & Condition
  • Privacy Policy
  • Cookie Policy
  • Contact us
  • Mail contact.anugal@businesscoresolutions.com

Phone

  • +31 6 50293414
  • +91 98848 16811
  • +1 (843) 252-4867

Mail

  • contact.anugal@businesscoresolutions.com
  • IGA
  • Terms & Condition
  • Privacy Policy
  • Cookie Policy
  • Contact us
Instagram Linkedin Youtube

© 2026 anugal. all rights reserveD

Sign in Create an Account

Lost your password?
  • Home
  • Platform
    • Identity Lifecycle Management
      • Joiner–Mover–Leaver (JML) AutomationAutomated lifecycle changes, zero delays
      • Birthright & Role Mapping Right access from day one.
      • Third-Party Identity GovernanceControl non-employee access seamlessly.
      • Machine & Non-Personal Identity Management Govern service and machine identities.
    • Access Requests & Controls
      • Self-Service Access RequestsFast requests with built-in controls
      • Approval & Access Control Engine Policy-driven approvals, consistent enforcement.
      • Emergency Access (Firefighter)Secure, time-bound privileged access.
      • Mass & Bulk Access RequestsManage access changes at scale
    • Access Intelligence
      • Access DiscoveryEnterprise-wide visibility into access
      • AI-Based Access RecommendationsAI-guided access decision support
      • Role Design & OptimizationOptimized roles and entitlement structure
      • My Access / My EntitlementsUser view of assigned access
    • Identity & Access Governance
      • Insights (Compliance & Security) Clear visibility into access risk.
      • Segregation of Duties (SoD) EnginePrevent conflicts before violations
      • Reports & Audit TrailsAudit-ready evidence, always available
      • Access CertificationsPeriodic reviews with full traceability
    • Integration & Automation
      • Orchestration StudioDesign identity workflows visually
      • Job SchedulerAutomate recurring identity operations
      • Third-Party & Service IntegrationsConnect systems without disruption
    • AI Agents
      • Anugal Co-PilotConversational access governance interface
      • Anugal.AI (Agentic Architecture)Agent-driven identity orchestration layer
  • Solutions
    • By Use Case & Outcome
      • Automate Joiner-Mover-Leaver (JML) LifecycleLifecycle-driven governed access automation
      • Simplify Access Requests & ApprovalsStructured, policy-driven access decisions
      • Enforce Segregation of Duties (SoD)Prevent conflicting access before execution
      • Accelerate Access Reviews & CertificationsContext-driven certification and review automation
      • Manage Machine & Third-Party AccessGovern non-human and external identities
      • Gain Real-Time Access IntelligenceContinuous visibility into identity risk
    • By Industry
      • Banking & Financial Services (BFSI)Govern financial access across systems
      • Healthcare & Life SciencesSecure clinical and research access
      • ManufacturingControl plant and operational identities
      • RetailGovern distributed workforce access
      • Consumer GoodsSecure supply chain identity operations
      • Public SectorControl access across government systems
    • By Regulation
      • SOXFinancial access control and auditability
      • GDPRPrivacy-driven identity access governance
      • HIPAAProtect healthcare access and data
      • PCI-DSSSecure payment system access controls
      • NIS2Strengthen cyber resilience governance
      • GxPControlled access for regulated environments
    • By Role
      • Security & Risk LeadersPrevent identity risk before exposure
      • Access & Identity ManagersCentralized lifecycle and access control
      • Compliance & Audit TeamsContinuous audit-ready governance evidence
      • IT Operations & Support Reduce manual access administration
      • Business & Application StakeholdersAccountable ownership of business access
  • Why Anugal
    • ROI Calculator
    • Time to Value
    • Agentic IGA Platform
    • Integration Catalog
    • Anugal vs Legacy vs Manual
  • Resources
    • Blog
    • Product Tours
    • White Papers
    • Solution Briefs
    • Webinars
    • Help Center
    • IGA Knowledge Hub
  • Company
    • Our Story
    • Partner with Us
    • Events
    • Success Stories
    • Newsroom
  • Request Demo