

SAP IDM after 2027 · 6 min read
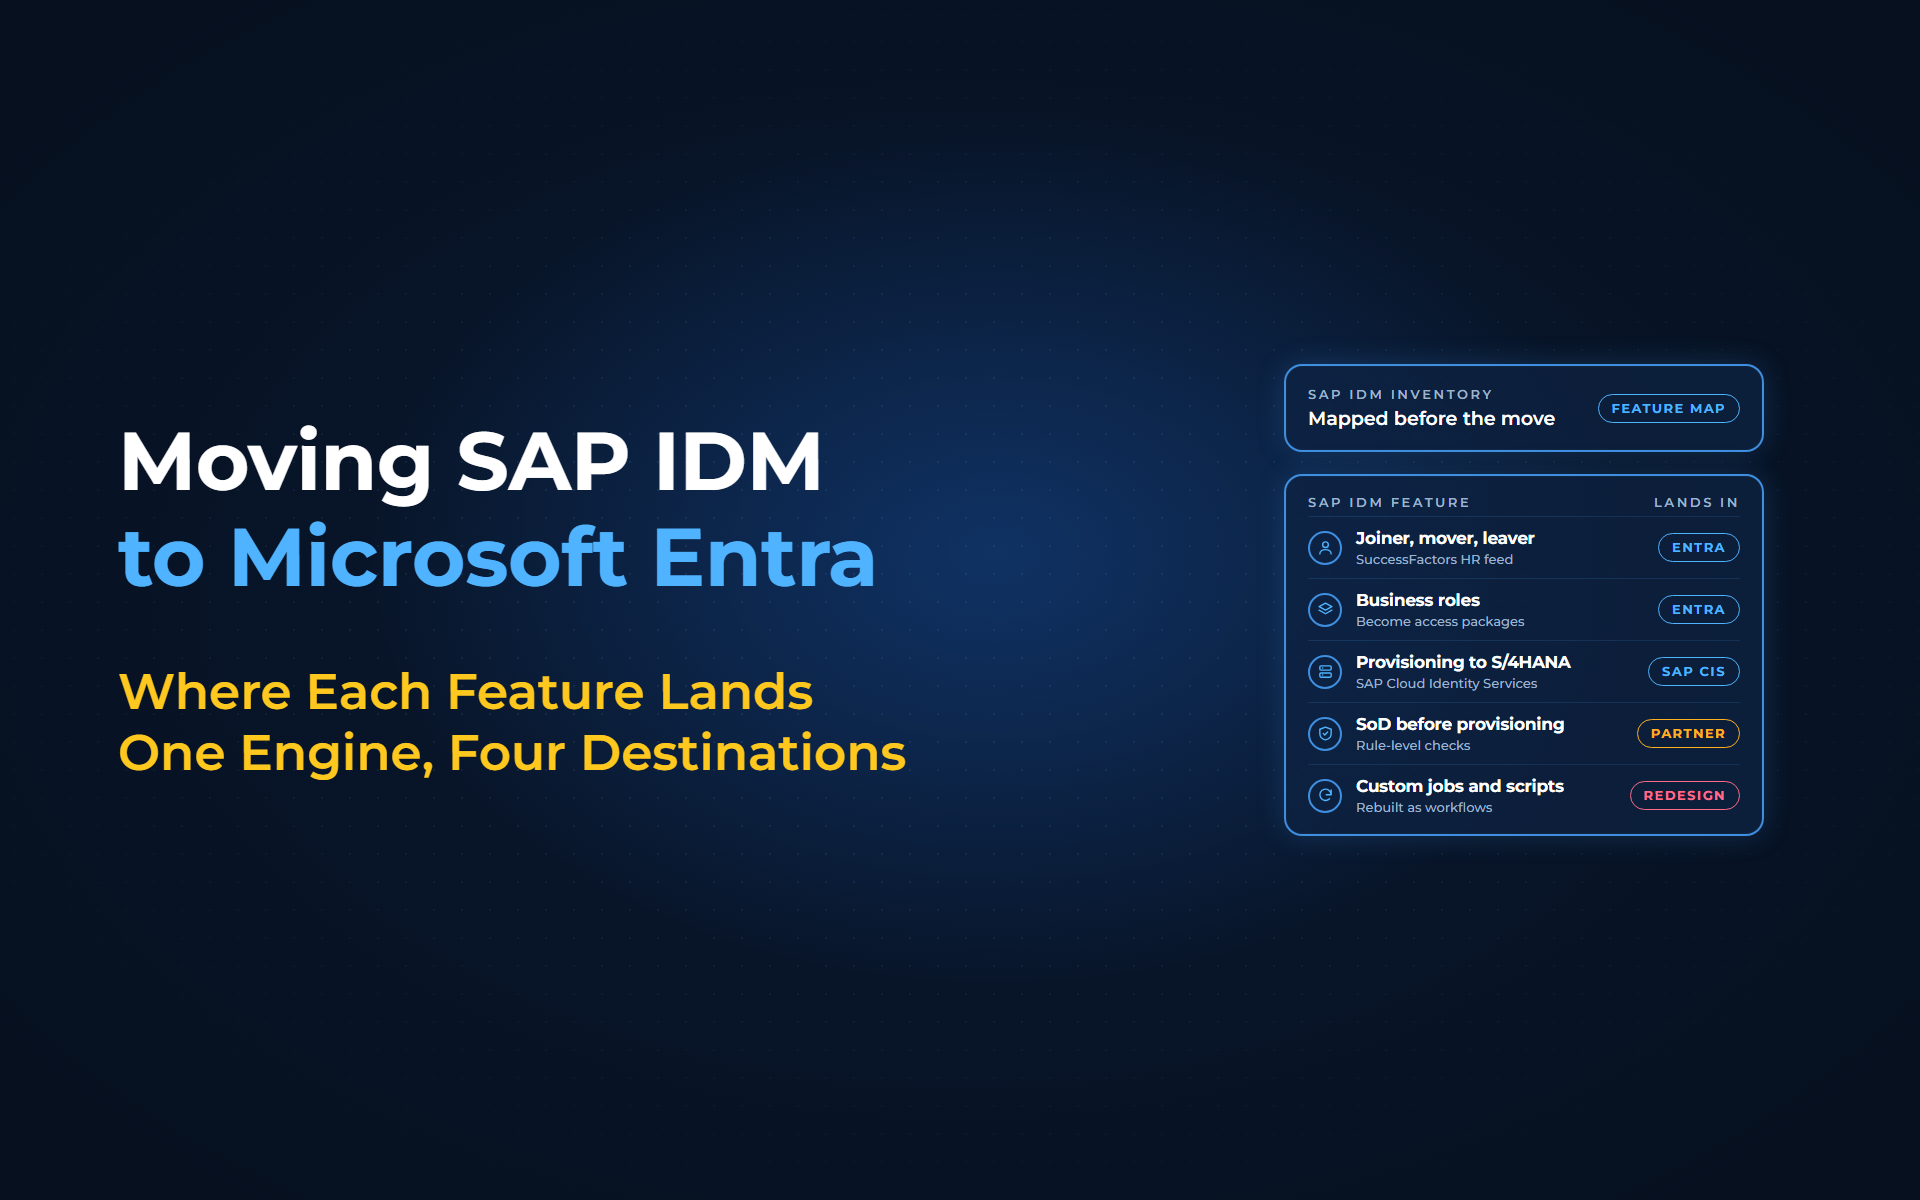
Where Each SAP IDM Feature Lands in Microsoft Entra
Moving SAP IDM to Microsoft Entra splits one engine 4 ways: some features land in Entra, some in SAP Cloud Identity Services, some need another vendor's product, and some need a redesign. With Anugal, the governance layer for SAP risk checks, emergency access and SAP-aware access reviews runs beside Entra, so your Microsoft tenant keeps doing the identity work.
The Head of IAM has the IDM inventory on screen: the SuccessFactors feed, SAP connectors, approval workflows, the GRC risk check and years of custom jobs. SAP ends mainstream maintenance for SAP Identity Management on 31 December 2027 (see our end-of-life timeline), so every line needs a new home.
Microsoft says its migration guidance "will be updated as new scenarios become available to migrate". If you have not picked a platform yet, start with our guide to choosing a platform.
Where does each feature land when you move SAP IDM to Microsoft Entra?
Of the 9 rows below, 6 land fully in Microsoft's or SAP's identity services.
| SAP IDM feature | Where it lands | What the documentation describes |
|---|---|---|
| HR-driven joiner, mover, leaver from SuccessFactors | Entra | Native connectors for hires, updates, terminations and rehires; mover access changes come from auto-assignment policies |
| Identity store and business roles | Entra | Business roles become access packages; technical roles become app roles or groups |
| Provisioning to SAP ECC | Entra | Provisioning agent and ECMA connector host calling SAP ECC web services that expose BAPIs; users only, not roles, profiles or passwords |
| Provisioning to S/4HANA | SAP Cloud Identity Services | Entra sends users and groups to SAP Cloud Identity Directory, which provisions groups as SAP roles; on-premise targets need the SAP Cloud Connector |
| Self-service requests and approvals | Entra | Access packages with multi-stage approval and expiry |
| Password reset (Logon Help) | Entra | Self-service password reset, with writeback to on-premises AD; the ECC connector has no password operations |
| SoD check before provisioning | Entra, plus another product for rules | Entra blocks incompatible access packages and groups; rule-level checks run elsewhere |
| Custom jobs and scripts | Redesign | Logic Apps callouts from lifecycle workflows and entitlement management |
| Role model | Redesign | Clean up outdated access rights and roles |
Which SAP IDM features need a partner product?
The SoD check that many SAP IDM setups requested from SAP access governance is the main one. Entra's own check compares whole bundles: a user "who already has an assignment to one access package can't request another access package." Anything deeper, Microsoft says, relies on "additional risk and fine-grained separation-of-duties checks enforced in those products", meaning SAP's own access governance or another vendor's tool connected to Entra.
Take a Vendor Maintenance bundle and a Payment Run bundle. If someone marks them incompatible, Entra stops one holder from requesting the other. The check reads bundle and group assignments, not whether the SAP roles inside 2 differently named bundles still add up to create-a-vendor-then-pay-it, in SAP or across a non-SAP application. That rule-level question is what the extra product answers.
Which SAP IDM features need a redesign, not a move?
Custom logic and the role model need a redesign. Microsoft says today's recommended approaches "will in many cases be different" from what organizations built for SAP IDM, and suggests using the move to "clean up and remove outdated integrations, access rights or roles".
On-premise S/4HANA adds work: SAP Learning notes that on-premise provisioning "requires a separate configuration in three places", the SAP BTP cockpit, the SAP Cloud Connector and the Identity Provisioning console.
How Anugal extends Microsoft Entra for SAP
With Anugal, Entra keeps the directory, sign-in and core lifecycle, and Anugal governs the SAP and cross-application decisions the map hands to a partner. Anugal connects to Microsoft Entra ID, SAP and other systems through pre-built connectors, and stops conflicting requests raised in Entra from moving through approval.
- Check SoD before access lands:
A configurable SoD risk library, with SAP rules down to transaction and authorization value, evaluates cross-application conflicts during access requests, role assignments and lifecycle events. High-risk combinations are blocked, routed for mitigation or escalated before provisioning. - Give reviewers SAP context:
Access reviews go to managers, application owners and entitlement owners, who see SoD conflicts, privilege level and usage. Rejected access is revoked automatically in connected systems. - Govern emergency access:
Firefighter access is approved, time-bound and recorded, then closed with a mandatory post-use review. - Clean the role model before it moves:
Role mining from real access patterns finds overlapping roles and entitlements that no longer belong, for role owners to confirm before anything is rebuilt in Entra. - Rebuild custom IDM logic as workflows:
Orchestration Studio lets you build governed workflows across directories, SAP systems, SaaS, legacy and custom applications.
Entra may be enough without a partner product. For a Microsoft-centric, cloud-first estate with light SAP customization, few legacy apps and no audit pressure on request-time SoD, Entra plus SAP Cloud Identity Services covers the map. Anugal also coexists with SAP GRC, so decide per control which tool owns it. You own the rule set and where each feature lands; your delivery partner plans and executes the transition.
From 1 SAP IDM engine to 4 clear destinations
Map every IDM feature to Entra, SAP Cloud Identity Services, a partner product or a redesign before you sequence the move. To see the partner layer run beside Entra on your own SAP roles, let's get you a working demo, or write to info.anugal@businesscoresolutions.com.
SAP IDM to Microsoft Entra: common questions
Does Microsoft Entra replace SAP IDM completely?
Not on its own. HR inbound from SuccessFactors, the identity store, requests and approvals, and ECC user provisioning move to Entra. Microsoft's ECC connector handles users only, with no roles, profiles or password operations, so ECC role assignment needs another path, and self-service password reset covers Entra and, with writeback, on-premises AD accounts. Provisioning into S/4HANA runs through SAP Cloud Identity Services, and fine-grained SoD is enforced in SAP access governance or partner products.
What does SAP Cloud Identity Services do in an SAP IDM to Microsoft Entra migration?
Entra provisions users and groups into SAP Cloud Identity Directory, and SAP Cloud Identity Services provisions them onward into SAP applications such as S/4HANA, where groups can become SAP roles. For on-premise S/4HANA, that path runs through the SAP Cloud Connector and needs configuration in 3 places.
Does Entra ID Governance check segregation of duties for SAP?
It checks between access packages and groups: a user who holds one package or group can be blocked from requesting an incompatible package. Microsoft says additional risk and fine-grained SoD checks are enforced in SAP access governance or partner products.
When is Microsoft Entra enough without a partner product?
Entra plus SAP Cloud Identity Services can cover the map for a Microsoft-centric, cloud-first estate with light SAP customization, few legacy apps and no audit pressure on request-time SoD.
Should SAP IDM custom scripts move to Entra as they are?
No. Microsoft says recommended approaches will in many cases differ from what organizations built for SAP IDM. Treat each script as a requirement, then rebuild it through Logic Apps callouts or governed workflows, and clean up outdated roles on the way.
Sources
- Microsoft Learn: Manage access to your SAP applications (https://learn.microsoft.com/en-us/entra/id-governance/sap). SuccessFactors inbound scenarios (hire, update, terminate, rehire, write-back); provisioning to SAP Cloud Identity Directory and on to S/4HANA On-Premise through the SAP cloud connector; ECC provisioning via the provisioning agent and the web services connector, with BAPIs exposed in SAP ECC; SoD checks and the "fine-grained separation-of-duties checks enforced in those products" quote.
- Microsoft Learn: Migrate identity management scenarios from SAP IDM to Microsoft Entra (https://learn.microsoft.com/en-us/entra/id-governance/scenarios/migrate-from-sap-idm). Microsoft and SAP collaboration and the "will be updated as new scenarios become available to migrate" quote; identity store mapping (business roles to access packages, technical roles to app roles or security groups); access package approvals, escalation and time limits; SSPR replacing SAP IDM Logon Help, with password writeback to on-premises AD DS; groups provisioned to SAP Cloud Identity Services and on as roles to other SAP applications; automatic assignment policies that add and remove access based on changes to user attributes; Logic Apps extensibility; the "will in many cases be different" and "clean up and remove outdated integrations, access rights or roles" quotes.
- Microsoft Learn: Configure separation of duties for an access package in entitlement management (https://learn.microsoft.com/en-us/entra/id-governance/entitlement-management-access-package-incompatible). Incompatible access packages and groups quote; license prerequisite Microsoft Entra ID P2, Microsoft Entra ID Governance or EMS E5.
- Microsoft Learn: Microsoft Entra provisioning into SAP ERP Central Component (SAP ECC, formerly SAP R/3) with NetWeaver AS ABAP 7.0 or later (https://learn.microsoft.com/en-us/entra/identity/app-provisioning/on-premises-sap-connector-configure). Provisioning agent with the ECMA connector host and generic web services connector; creates, removes and updates users in SAP ECC; out of scope: local activity groups, roles and profiles, and password operations.
- SAP Learning: Identifying Provisioning Services Operations (Introducing SAP Cloud Identity Services) (https://learning.sap.com/courses/introducing-sap-cloud-identity-services/identifying-provisioning-services-operations_cd33439b-c544-47b3-8df2-7bdd8fe2e0d3). On-premise provisioning "requires a separate configuration in three places": SAP BTP cockpit, SAP Cloud Connector and the Identity Provisioning administration console.
- Anugal: SAP IDM End of Life 2027: What It Means and Why to Act Now (https://anugal.ai/sap-idm-end-of-life/). SAP ends mainstream maintenance for SAP Identity Management on 31 December 2027; a one-time paid extension runs to 2030.
- Anugal: SAP IDM Replacement: Microsoft Entra vs a Full IGA Platform (https://anugal.ai/sap-idm-replacement/). Anugal extends governance beside Entra; Entra is defensible for a cloud-first company with light SAP customization and few legacy apps.
- Anugal: Segregation of Duties Enforcement (https://anugal.ai/enforce-segregation-of-duties-sod/). Configurable SoD risk library evaluating cross-application conflicts during requests, role assignments and lifecycle events; block, mitigate or escalate before provisioning; documented, time-bound mitigations.
- Anugal: Access Certifications (https://anugal.ai/access-certifications/). Reviews routed to managers, application owners and entitlement owners; SoD conflicts, privilege level, usage and plain-language descriptions; automatic revocation across target systems.
- Anugal: Emergency Access Management (https://anugal.ai/emergency-access-firefighter/). Just-in-time emergency access that is approved, time-bound, recorded, with mandatory post-use review.
- Anugal: Role Design Optimization (https://anugal.ai/role-design-optimization/). Role mining from real access patterns; identification of overlapping roles and entitlements that no longer belong.
- Anugal: Orchestration Studio (https://anugal.ai/orchestration-studio/). Governed workflows built and run across directories, SAP systems, SaaS platforms, legacy and custom applications.
- Anugal: FAQs (https://anugal.ai/faqs/). Pre-built connectors for SAP and Azure AD; coexistence with incumbent identity and access management solutions and with SAP GRC.