Leaving SAP IdM?
Anugal vs Microsoft Entra for SAP access governance
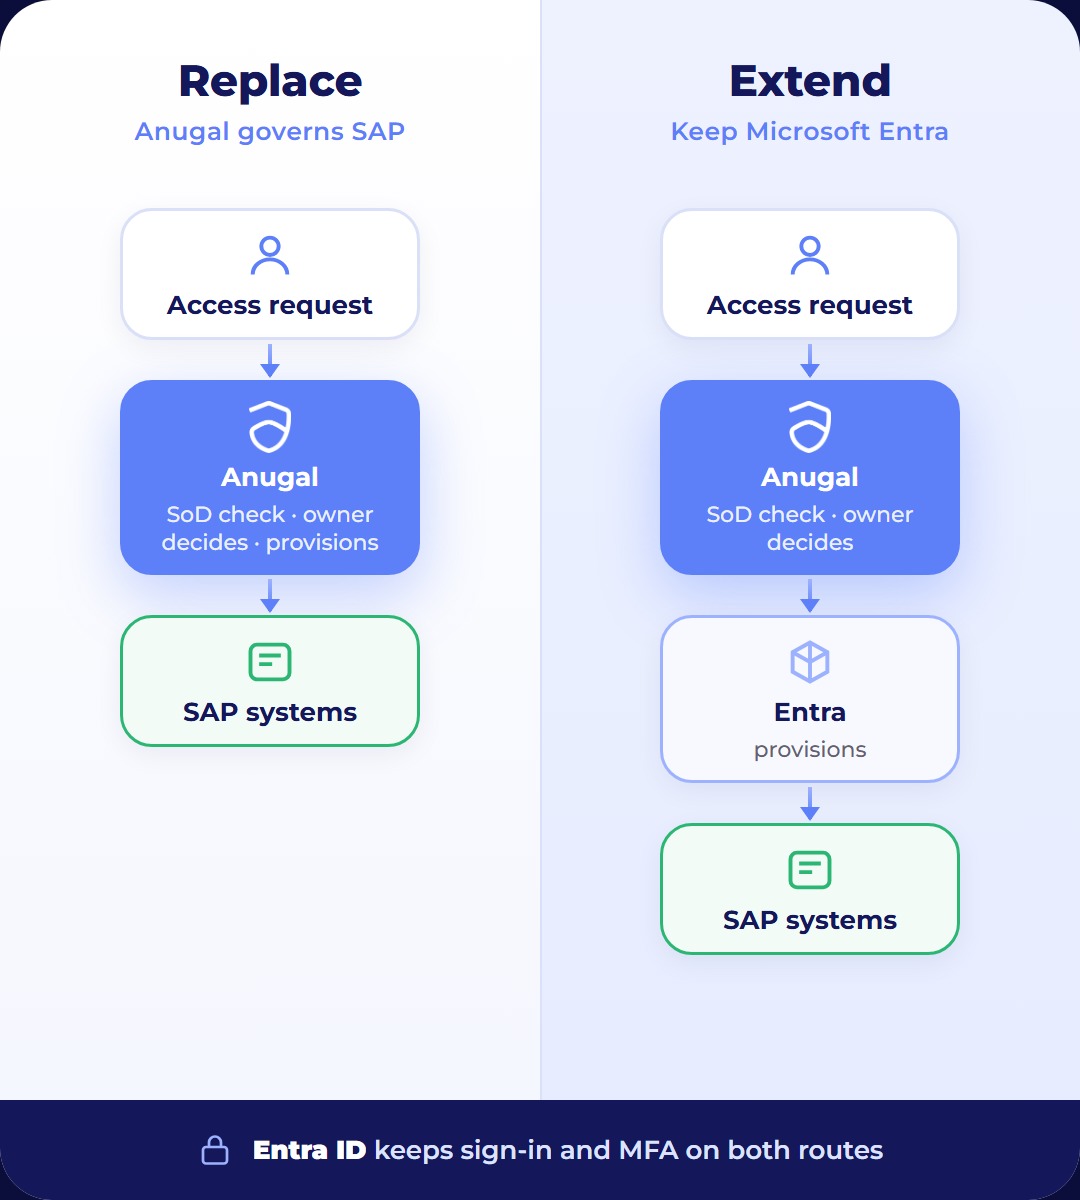
There are two ways to leave SAP IdM with Anugal. With the Replace route, you govern SAP access in Anugal. With the Extend route, you keep Microsoft Entra ID Governance, and Anugal checks end-to-end, cross-system segregation of duties (SoD) before Entra provisions access. On both routes, Entra ID continues to handle sign-in and MFA.
Entra is one SAP IdM exit, but who owns the SAP access decision?
Choose the route that fits your Entra plans
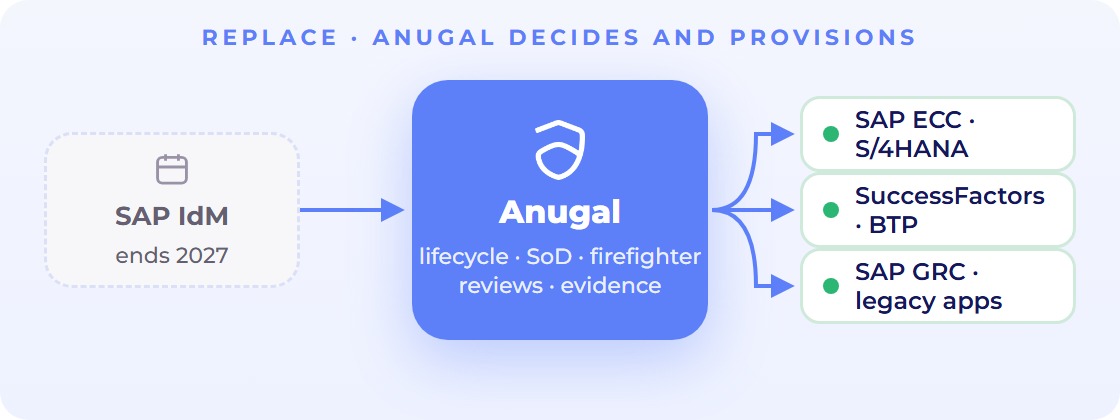
Replace: govern SAP access in Anugal
- Lifecycle, end-to-end, cross-system SoD, SAP firefighter, reviews and evidence in one platform.
- Bi-directional adaptors for SAP ECC, S/4HANA, SuccessFactors, BTP and SAP GRC.
- Orchestration Studio reaches legacy and custom applications.
Best for: SAP access risk drives the project, and most of your SAP IdM targets are SAP or legacy systems.
Trade-off: if Entra still governs Microsoft resources, you run two governance tools side by side. Entra keeps sign-in and MFA either way.
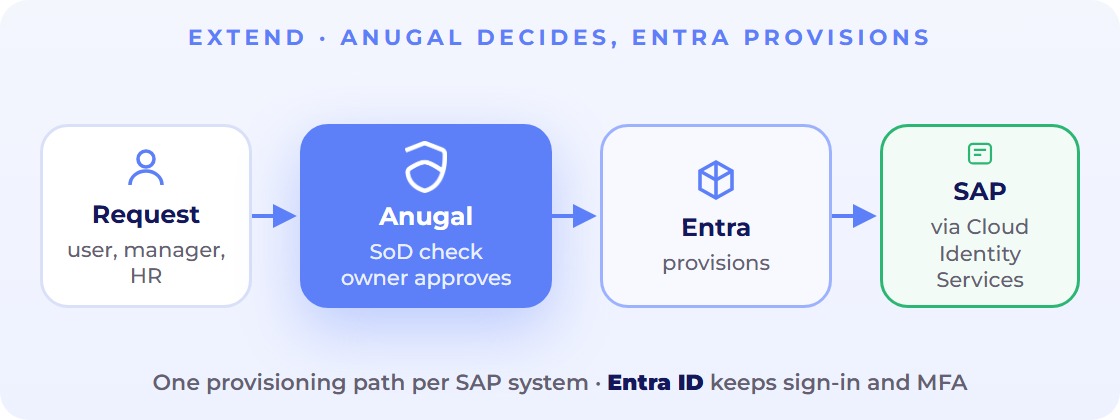
Extend: keep Entra and add Anugal’s SoD check
- Anugal checks end-to-end, cross-system SoD and routes each SAP request to an accountable owner before Entra provisions access.
- Entra provisions the SAP user; roles reach SAP through SAP Cloud Identity Services, as Microsoft documents.
- Each SAP system keeps a single provisioning path, so Anugal and Entra never provision the same system.
- Owners make SAP firefighter and revoke decisions in Anugal; Entra carries them out on the same provisioning path.
Best for: you already run Entra ID Governance, and SAP is the hard part.
Trade-off: two products, so agree which one decides and which one provisions each SAP system.
What you get on either route
Decide before access is granted.Conflicts are blocked, escalated or routed for mitigation. AI recommends; accountable owners decide.
Control emergency SAP access.SAP firefighter is approved, time-bound, scoped and reviewed after use.
Keep the evidence.Decisions made through Anugal become immutable audit records.
Anugal vs Microsoft Entra at a glance
| Capability | Microsoft Entra ID Governance | Anugal |
|---|---|---|
| SAP systems reached | Connectors to SAP ECC, SAP Cloud Identity Services and SuccessFactors. Microsoft lists S/4HANA On-Premise through SAP Cloud Identity Services; for SAP roles it points to SAP Cloud Identity Services. | Bi-directional adaptors for SAP ECC, S/4HANA, SuccessFactors, BTP and SAP GRC. |
| Joiner, mover, leaver | SuccessFactors events create, update and disable Entra ID accounts, then users are provisioned into SAP applications. | Joiners get only what their role justifies; movers lose obsolete permissions; leavers lose access across applications. |
| SoD before access is granted | Blocks requests incompatible with an access package or group the user already holds, and describes SoD checks “across their financial and other business-critical applications, along with Microsoft Entra integrated applications”. For “additional risk and fine-grained separation-of-duties checks”, points to SAP access governance and partner products. | End-to-end, cross-system SoD across SAP and non-SAP systems, enforced before approval. |
| Emergency and privileged access (SAP firefighter) | Privileged Identity Management: just-in-time, time-bound and approval-based activation of privileged roles in Entra ID, Azure and other Microsoft Online Services, and for groups; justification, MFA and audit history. | Just-in-time, approved, time-bound and scoped; monitored; reviewed after use. |
| Vendors, contractors, non-human identities | Guests can get access packages; Microsoft Agent 365 governs agents and service principals. | Third-party access is time-bound and policy-checked; service accounts carry an owner and purpose. |
| Systems without modern APIs | SCIM, SOAP or REST, PowerShell or ECMA connectors; ServiceNow tickets where no provisioning interface exists. | Orchestration Studio across SAP, SaaS, legacy and custom applications; RPA where no API exists. |
| Access reviews and AI | Recurring reviews where reviewers decide “with the help of smart recommendations”. | Reviews show risk context and AI recommendations, and revoke rejected access automatically (in Extend, through Entra). |
| Audit evidence | Built-in reports and Azure Monitor workbooks on audit, sign-in and provisioning logs; Entra keeps audit logs for 30 days (P1/P2); longer retention means routing them to Azure Monitor or storage. | Decisions made through Anugal kept as immutable audit records. |
| Alongside SAP GRC or SAP IAG | SAP IAG integration, which Microsoft lists as Preview. Microsoft says capabilities of both products “continue to evolve”, including Entra integrations with SAP Access Control and SAP IAG. | Runs beside SAP GRC. |
Microsoft details are taken from Microsoft’s public documentation.
How the Extend route works
Anugal checks, owners approve, and Entra provisions.
Questions about Anugal and Microsoft Entra
Can Microsoft Entra replace SAP IdM, or only part of it?
For lifecycle and provisioning, Microsoft documents a migration path from SAP IdM, with connectors to SAP ECC, SAP Cloud Identity Services and SuccessFactors. For “additional risk and fine-grained separation-of-duties checks”, Microsoft points to SAP access governance and partner products. Where SoD, SAP firefighter and SAP access evidence are decided is a separate choice from provisioning.
Does Entra ID Governance check SAP segregation of duties before access is granted?
Microsoft documents that entitlement management can block a request incompatible with an access package or group the user already holds, and names SAP access governance and partner products for additional risk checks. With Anugal, end-to-end, cross-system SoD is checked across SAP and non-SAP systems before access is approved.
We already have Entra ID Governance. Can we keep it and add Anugal?
Yes. With Anugal’s Extend route, Anugal connects with Entra and checks SoD, and your owners approve SAP access. Entra then provisions the SAP user, with roles reaching SAP through SAP Cloud Identity Services as Microsoft documents, so each SAP system has one provisioning path.
Can Anugal replace Entra ID Governance for SAP access governance?
Yes. With Anugal’s Replace route, SAP access lifecycle, end-to-end, cross-system SoD, SAP firefighter, access reviews and audit evidence run in one platform. Bi-directional adaptors for SAP ECC, S/4HANA, SuccessFactors and BTP handle role assignment directly, and Anugal runs beside SAP GRC. Entra ID stays your identity provider for sign-in and MFA.
How does each product handle SAP firefighter or emergency access?
Microsoft documents Privileged Identity Management for just-in-time, time-bound and approval-based privileged access in Microsoft Entra ID, Azure, other Microsoft Online Services and groups. With Anugal, SAP firefighter access is just-in-time, approved, time-bound, scoped to specific systems or roles, monitored, and reviewed after use.
Is the Entra integration with SAP IAG generally available?
Not as of 3 November 2026. Microsoft lists its integration with SAP Cloud Identity Access Governance (IAG) as Preview, and says it requires “Microsoft Entra ID Governance or Microsoft Entra Suite licenses”, SAP Cloud Identity Services integrated with Entra, and an “SAP Cloud Identity and Access Governance (IAG) tenant license”.
See both routes on your SAP estate
Bring your SAP systems and Entra plans. We’ll show you which route fits.