How to Prove Who Had SAP Access When a DORA Incident Happened
After a DORA incident, the first question is who had access to the affected SAP system at the time. Here is why today’s access report cannot answer it, and what to record so you can.

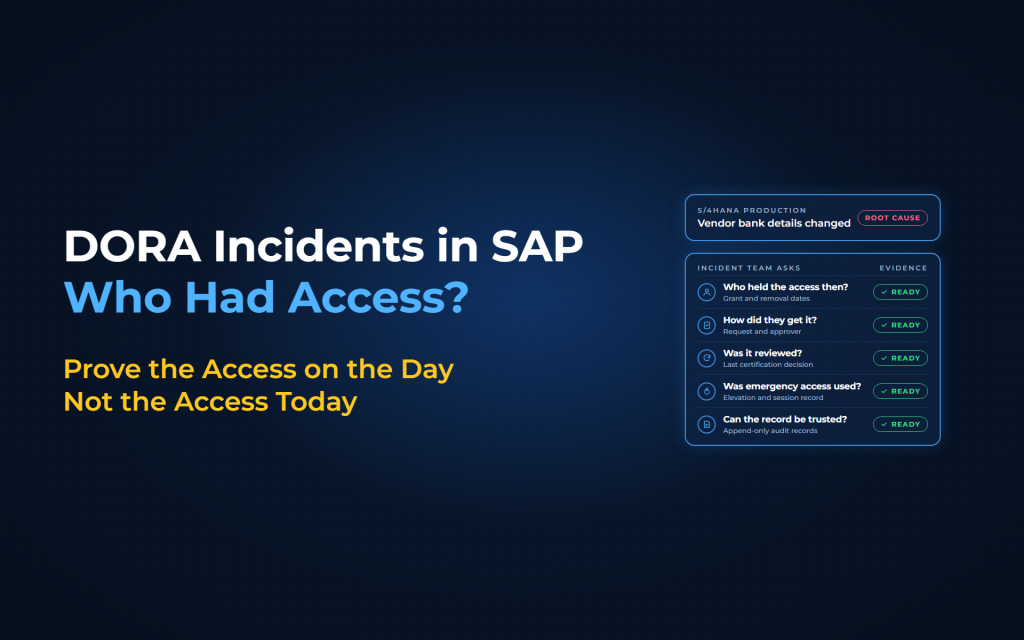
After a DORA incident, the first question is who had access to the affected SAP system at the time. Here is why today’s access report cannot answer it, and what to record so you can.
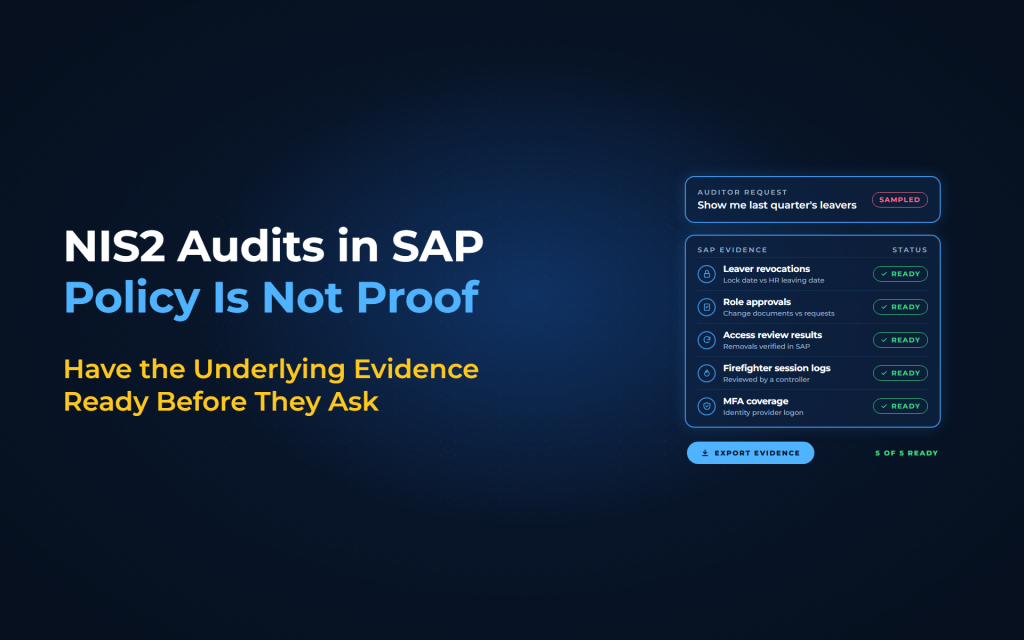
NIS2 lets supervisors ask for the underlying evidence behind your access policy. Here is what that means in SAP, row by row.
Identity Evidence and Auditability Under CSRD and EU Sustainability Reporting CSRD assurance under ISSA 5000 requires testing of the internal controls that produce sustainability data. That includes who has access, whether duties are segregated, and whether changes are logged. Four identity artifacts answer those tests: provisioned access with justification, enforced segregation of duties, periodic access […]