

SAP access risk · 6 min read
Why Preventive SoD Must Run Before Access Is Granted, and Where Entra Stops
Preventive SoD (segregation of duties) stops a conflicting access request before anything is provisioned into SAP. Microsoft Entra ID Governance can block incompatible access packages, but Microsoft's own SAP guidance leaves fine-grained SAP risk checks to SAP access governance and partner products. With Anugal, that check runs at request time across SAP and non-SAP applications.
An accounts payable clerk already holds the AP payment processing access package in Entra. She requests vendor maintenance for a supplier project, her manager approves, and the access reaches S/4HANA through SAP Cloud Identity Services. Nobody had marked the 2 packages as incompatible. By the next audit, she can create a vendor and approve the payment to it.
What does separation of duties in Microsoft Entra check?
Entra compares memberships, not permissions. Microsoft describes the setting:
"With the separation of duties settings on an access package, you can configure that a user who is a member of a security group or who already has an assignment to one access package can't request another access package."
It is a useful guardrail with 3 limits for SAP:
- It compares packages and groups:
It checks which access packages or security groups a user holds, not what the SAP role inside a package allows. - It works in 1 direction:
Each incompatible relationship is unidirectional, so a mutual block means configuring both packages. - It lists existing conflicts:
Users who already hold both packages appear in a downloadable list. They keep the access but cannot re-request it.
Where does Microsoft place fine-grained SAP SoD checks?
Beyond package checks, Microsoft's SAP page lists integrations with SAP's governance products and with partners, and says the extra risk analysis and finer SoD rules are "enforced in those products". The fine-grained SAP decision therefore sits outside Entra, with Entra as the front door.
Why does preventive SoD have to work at the authorization level?
SAP decides what a user can do from authorizations, not package names. SAP checks the object S_TCODE when a GUI transaction starts (Fiori apps add start checks such as S_SERVICE), and programs run AUTHORITY-CHECK against the user's authorizations. A rule that sees only 2 package names cannot tell whether they let someone create a vendor and pay it through the F110 payment run.
A package name is not a permission. SAP checks transactions and authorization values, so that is where an SoD rule has to look.
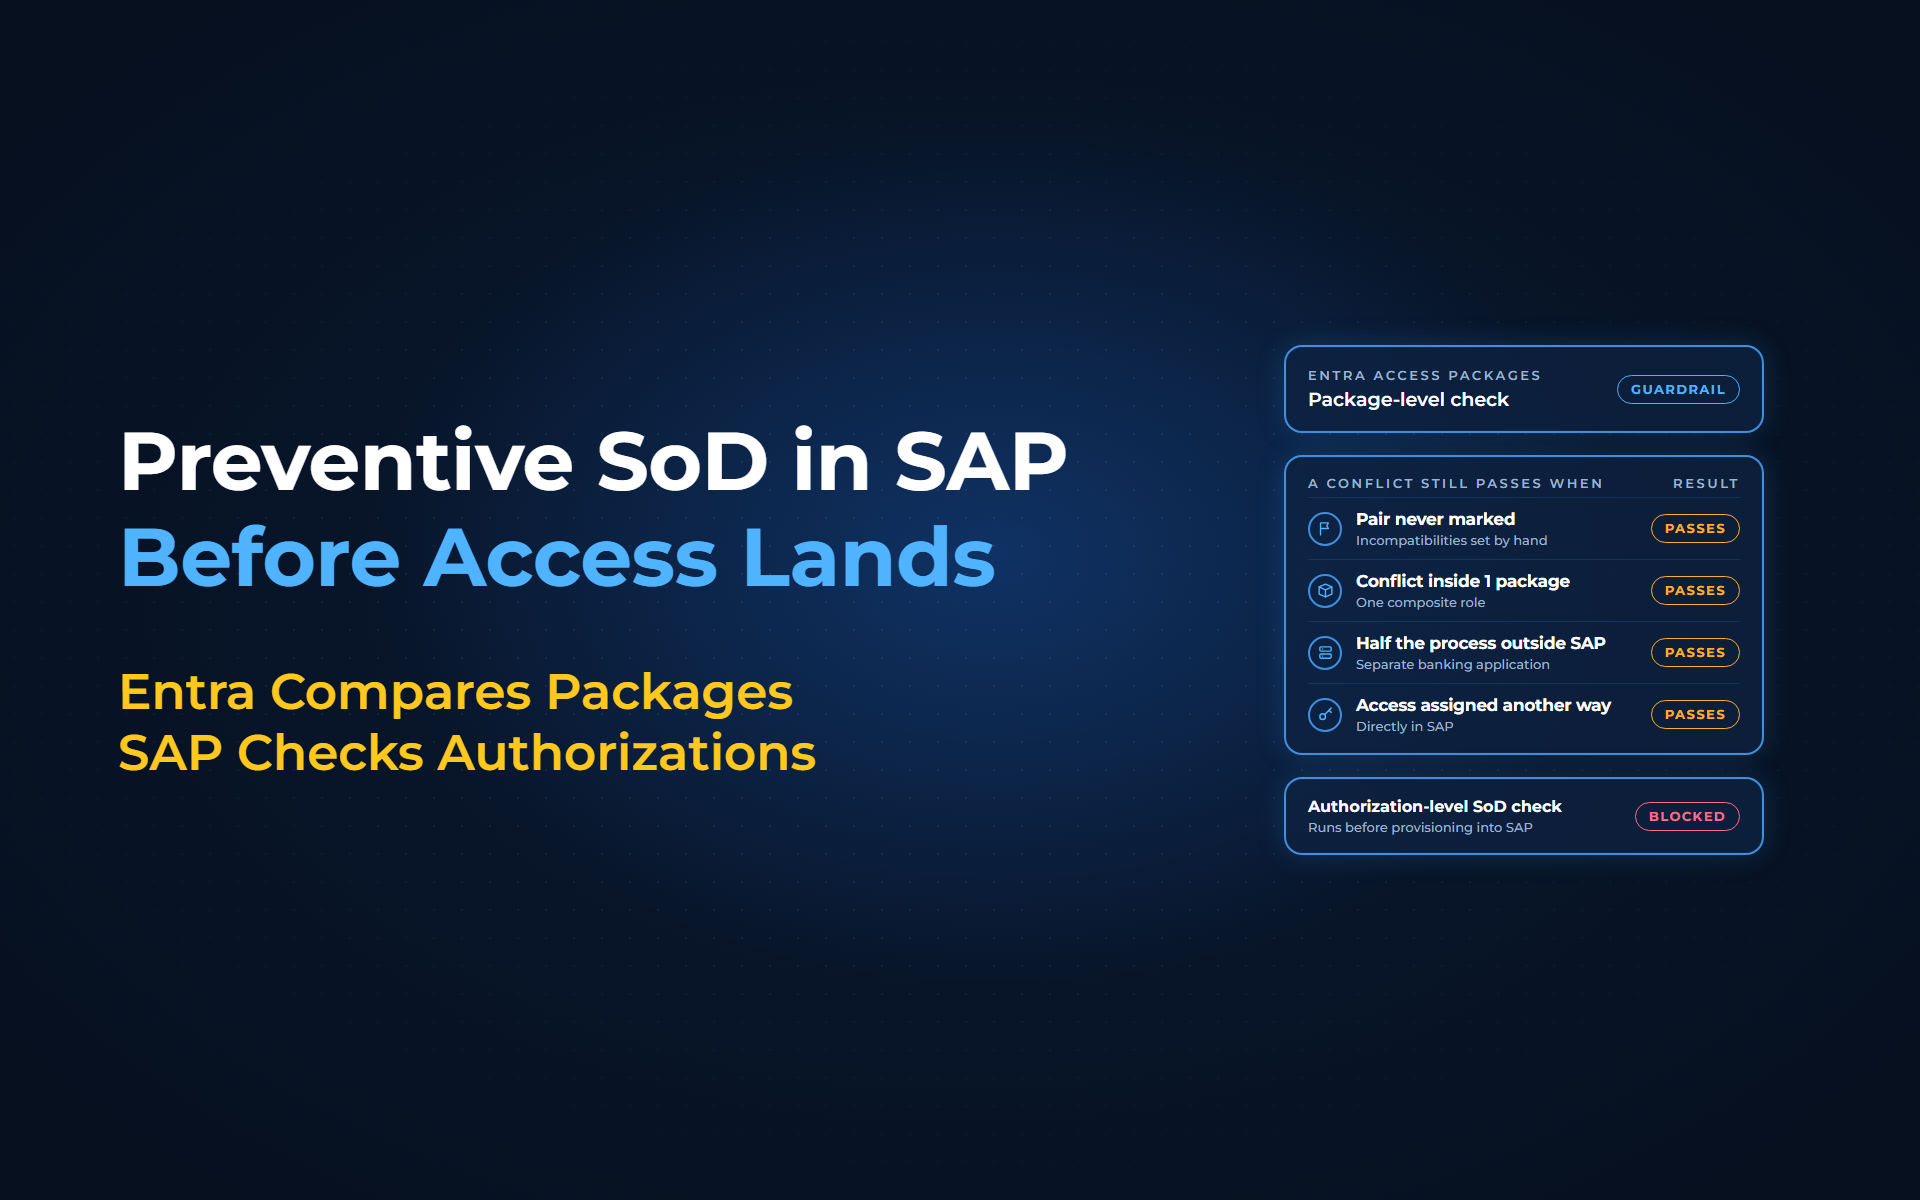
The clerk's conflict can pass a package-level rule in 4 ways:
- The pair was never marked:
Incompatibilities are marked package by package, so a new package or a combination nobody anticipated passes. A function-level rule covers every role that grants the function. - The conflict sits inside 1 package:
If one composite role carries both vendor maintenance and payment authorizations, there is nothing to compare. - Half the process runs outside SAP:
If payments are released in a separate banking application, each package looks harmless alone. - The access arrives another way:
An administrator who assigns an application role outside entitlement management skips the package check. Microsoft's Application role assignment activity workbook shows those assignments only after they happen.
How Anugal adds preventive SoD beside Microsoft Entra
Keep Entra for lifecycle, single sign-on and access packages. Anugal connects to SAP and Microsoft Entra ID through pre-built connectors and stops conflicting Entra requests from moving through approval. With Anugal, the SoD decision happens at request time across connected applications:
- Check every request against 1 risk library:
A configurable SoD risk library evaluates cross-application conflicts during access requests, role assignments and lifecycle events. Her request is tested against what she holds in SAP and the payment application. Rules can target SAP transactions and authorization values. - Stop the conflict before provisioning:
High-risk combinations are blocked, routed for mitigation or escalated based on policy before access is provisioned. Approval routing follows sensitivity, ownership and policy, not only the reporting line. - Govern the exception:
If the project needs her to hold both, a compensating control with a named owner and expiry is attached, documented and traceable. - Keep the evidence:
Risk evaluations, mitigations and approvals are kept as structured audit records that link each change to its SoD evaluation.
| SoD check | Entra incompatible access packages | With Anugal |
|---|---|---|
| What is compared | Access package and security group memberships | SAP transactions and authorization values, plus access in other connected applications |
| When it runs | When a package is requested or assigned | Requests, role assignments and lifecycle events, before provisioning |
| Exceptions | A separate combined access package; its policy can add approval and expiry | Compensating control with owner, scope and expiry |
| Evidence | Access package activity workbook in Azure Monitor | Structured audit records tied to each SoD evaluation |
Anugal checks against the rules you configure, so your SAP security and audit teams still own the rule set and every risk acceptance. Anugal coexists with SAP GRC and incumbent identity platforms. For a Microsoft-centric estate with little SAP and few SoD obligations, Entra's package check may be enough.
See a conflicting request stopped
From package-level blocks to preventive SoD you can prove
Entra tells you which packages should not sit together. Your auditor asks whether one person could create a vendor and pay it. Answer that at request time, at the authorization level and across every connected system in the process. To see the clerk's request stopped before it reaches S/4HANA, let's get you a working demo, or write to info.anugal@businesscoresolutions.com.
Preventive SoD and Microsoft Entra: common questions
What is preventive SoD?
Preventive SoD is a segregation of duties check that runs when access is requested or assigned, before it is provisioned. A conflicting combination is blocked, routed for mitigation or escalated before anyone holds the access.
Does Microsoft Entra ID Governance support separation of duties?
Yes, at the access package level. You can mark other access packages or security groups as incompatible, so a user who already holds one cannot request the other. Each relationship works in 1 direction, so a mutual block means configuring both packages.
Can Microsoft Entra check SoD inside SAP roles?
Not on its own. Microsoft's SAP guidance says additional risk and fine-grained separation-of-duties checks are enforced in SAP access governance and partner products that integrate with Entra access packages.
Why is an access package rule not enough for SAP SoD?
SAP grants activity through transactions and authorization values inside roles. A package rule sees only package and group memberships, so a conflict inside one package, a pair nobody marked, or a risk spanning SAP and a non-SAP application can pass.
Does Anugal replace Microsoft Entra?
No. Entra stays the identity platform for lifecycle, sign-on and access packages. Anugal adds a configurable cross-application SoD risk library that evaluates requests, role assignments and lifecycle events before access is provisioned and records each decision.
Sources
- Microsoft Learn: Configure separation of duties for an access package in entitlement management (https://learn.microsoft.com/en-us/entra/id-governance/entitlement-management-access-package-incompatible). The separation of duties setting quoted in the post, the license prerequisites, unidirectional incompatibility, the downloadable list of existing incompatible assignments, the combined access package for overrides, and the Azure Monitor workbooks (Access Package Activity and Application role assignment activity).
- Microsoft Learn: Manage access to your SAP applications (https://learn.microsoft.com/en-us/entra/id-governance/sap). Separation of duties checks in entitlement management, additional risk and fine-grained checks enforced in SAP access governance and partner products and provisioning to S/4HANA through SAP Cloud Identity Services.
- Microsoft Learn: New name for Azure Active Directory (https://learn.microsoft.com/en-us/entra/fundamentals/new-name). Azure AD was renamed Microsoft Entra ID.
- SAP Help (older release, NetWeaver 7.3): Authorization checks (https://help.sap.com/doc/saphelp_nw73/7.3.16/en-US/4c/a0ac7a68243b9ee10000000a42189b/content.htm). Transaction start check through S_TCODE and program checks through AUTHORITY-CHECK against the user's authorizations.
- SAP Learning: Exploring the Authorization Concept for SAP Fiori on SAP S/4HANA, Analyzing Missing Authorizations (https://learning.sap.com/courses/exploring-the-authorization-concept-for-sap-fiori-on-sap-s-4hana/analyzing-missing-authorizations). Start authorization checks for SAP Fiori OData services through the authorization object S_SERVICE.
- SAP KBA 3761846: Special G/L down payments not considered in F110 selection (https://userapps.support.sap.com/sap/support/knowledge/en/3761846). F110 as the SAP automatic payment program used in the example.
- Anugal: Enforce Segregation of Duties (https://anugal.ai/enforce-segregation-of-duties-sod/). Configurable SoD risk library, cross-application evaluation during access requests, role assignments and lifecycle events, block, mitigate or escalate before provisioning, time-bound mitigations and structured audit records.
- Anugal: Segregation of Duties (SoD) Engine (https://anugal.ai/segregation-of-duties-sod-engine/). Evaluation against enterprise-wide SoD rules, compensating controls with ownership and expiry, and evidence linking access changes to SoD evaluation and justification.
- Anugal: Simplify Access Requests and Approvals (https://anugal.ai/simplify-access-requests-approvals/). Eligibility, SoD and risk checks enforced before access is granted, and approval routing by sensitivity, ownership and policy.
- Anugal: FAQs (https://anugal.ai/faqs/). Pre-built connectors for SAP and Azure AD, and coexistence with SAP GRC and incumbent identity platforms.
- Anugal: SAP Security Layers, IGA vs Threat Detection (https://anugal.ai/sap-security-layers-iga-vs-threat-detection/). The vendor creation and payment approval conflict used in the example.