

SAP GRC 2027 · Article 7 of 8 · Quick Read
Your Biggest SAP Access Risk May Sit Outside SAP
An SAP upgrade does not automatically remove access from every connected application.
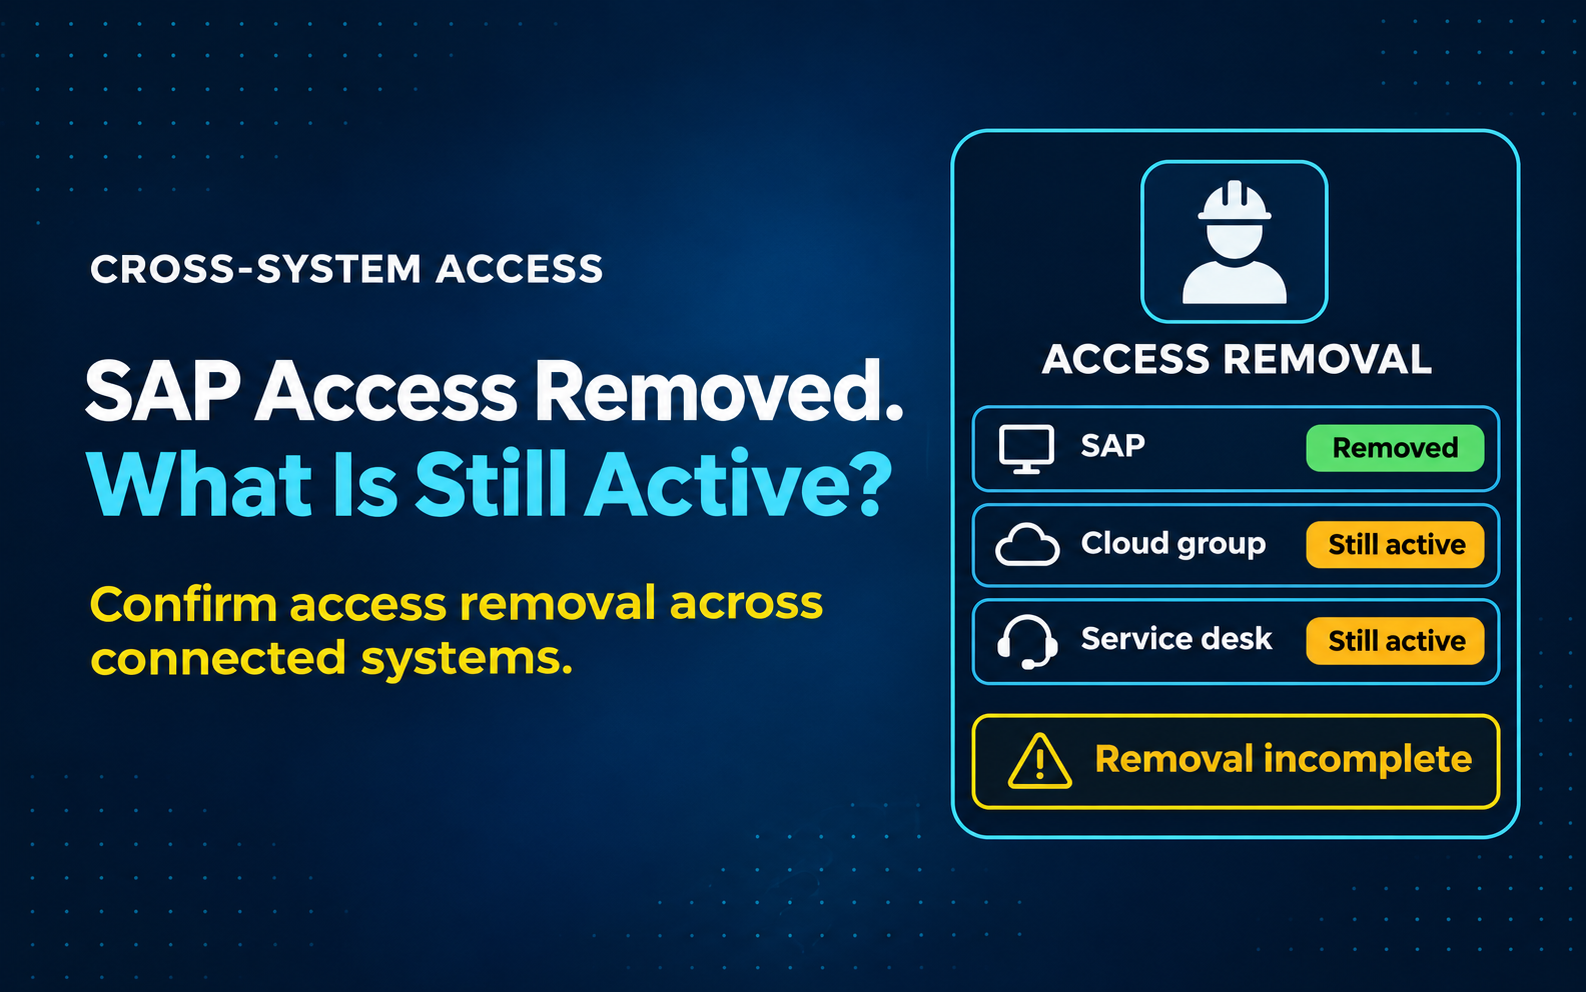
A contractor finishes their assignment. SAP access is removed on Friday. Their cloud group and service desk account remain active through the following week.
The offboarding ticket says Complete. Your risk is not.
Why SAP-only thinking misses the issue
HR owns the departure date. IT owns the directory. SAP Security owns the ERP account. Application teams own everything else. Each group acts on a different system and schedule. Nobody sees the full access outcome.
An SAP GRC version change supports SAP continuity. It does not, by itself, prove that every non-SAP entitlement follows the same removal decision.
An identity is only offboarded when the connected access is actually gone.
Find the gaps with one contractor
- List the identity’s SAP, directory, SaaS, cloud, and legacy accounts.
- Identify who triggers and approves each removal.
- Check which target systems confirm the change, and which only close a ticket.
- Test what happens when a connector fails or a local account remains active.
Repeat the test for a department transfer and a temporary privileged role. These two events expose access that ordinary offboarding checks miss.
How Anugal supports cross-system governance
Anugal provides identity lifecycle and access orchestration across SAP and supported non-SAP applications. Anugal Studio helps structure controlled workflows around different integration methods. Agentic AI can assist users and reviewers with request context, risk signals, and exception handling; system permissions and approval rules still govern every action.
Begin with a few high-risk systems and prove completion before expanding the scope.
Access risk outside SAP: common questions
Does an SAP GRC upgrade remove access in non-SAP systems?
No. An SAP GRC version change supports SAP continuity. It does not, by itself, prove that every non-SAP entitlement follows the same removal decision.
How do you find cross-system offboarding gaps?
Take one contractor. List their SAP, directory, SaaS, cloud, and legacy accounts, identify who triggers and approves each removal, check which systems confirm the change, and test what happens when a connector fails.
Does Microsoft Entra ID alone solve this?
Entra ID handles important identity functions. You still need to verify application-level entitlements, SoD controls, and completed deprovisioning.
See how Anugal can support your GRC modernization
Talk to us: hello@businesscoresolutions.com